February 16, 2026 · Hugh Carroll
The State of API Security in 2026: Analysis of real-world API vulnerabilities
Our recently published State of API Security Report 2026﹡ delivers a data-driven analysis of real-world API vulnerabilities, showing how common mistakes in implementation translate into security risks in production. It paints a clear and, at times, uncomfortable picture: despite years of awareness, tooling, and guidance, the same core API security failures continue to show up in real-world exploits. APIs now sit at the center of enterprise risk. They power digital services, connect partners, and increasingly act as the integration layer for AI systems and autonomous agents. That makes API security not just a development concern, but a board-level issue. What’s changed is the scale, speed, and impact—especially as organizations move toward AI-driven systems that rely heavily on APIs.
Analysis of vulnerabilities reported across 2024–2025 shows that the top five OWASP categories account for the majority of observed issues, reinforcing that attackers are still succeeding with well-known techniques.
At the top of the list is Broken Object Level Authorization (BOLA), which represents the single largest category of reported API vulnerabilities. Closely following are Broken Authentication, Broken Object Property Level Authorization (BOPLA), and Broken Function Level Authorization (BFLA). Together, authorization-related flaws dominate the threat landscape.
BOLA alone accounts for nearly half of authorization-related findings, with BFLA contributing just over 40%, and authorization bypass techniques making up the remainder.
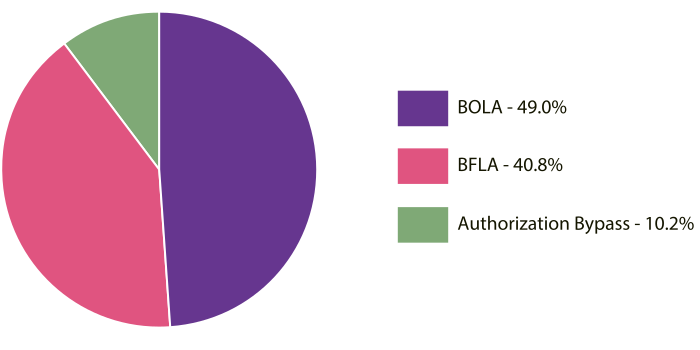
API Authorization vulnerabilities 2024-2025. Copyright © 42Crunch 2026.
The takeaway for security and engineering practitioners alike is pretty obvious: most API breaches are not caused by sophisticated exploits, but by missing or incorrect authorization checks on legitimate endpoints.
APIs are deceptively complex. Each endpoint can support multiple HTTP methods, each method can act on different resources, and each resource may require different permissions depending on context. As APIs evolve, that complexity compounds.
The report highlights that many BFLA cases stem from basic role-based access control errors, where functions intended only for privileged users are exposed to broader roles. In one cited real-world example, a sensitive password backup function was accessible to non-admin users via the API, despite being restricted in the UI.
For large enterprises, this points to a structural problem: security controls are often enforced inconsistently between UI, backend services, and APIs. Client-side controls give a false sense of security, while APIs—designed for reuse and integration—become the weakest link.
Authentication failures remain another major contributor to API risk. The report documents recurring issues such as:
What’s notable here is that these weaknesses often exist not because teams don’t know better, but because APIs are developed, deployed, and modified faster than security controls are reviewed. In large organizations with hundreds or thousands of APIs, gaps are inevitable without automation and governance.
Beyond Authentication and Authorization, the report also points to malicious input—including injection attacks and path traversal—as a persistent driver of API vulnerabilities. Some of these issues fall outside the current OWASP API Top 10 but still show up regularly in real-world findings .
Equally important are misconfigurations beyond the API code itself:
For enterprise teams, this reinforces a key lesson: API security is not just a coding problem—it’s a lifecycle and operational problem.
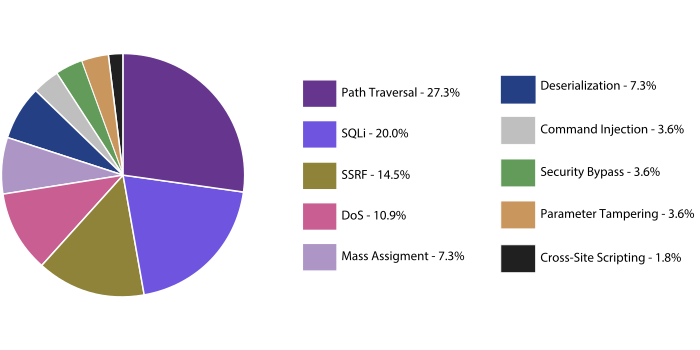
API Input Validation Flaws 2024-2025. Copyright © 42Crunch 2026.
The report makes it clear that AI will materially change the risk profile for APIs in 2026 and beyond.
AI systems—and especially agentic AI—consume APIs differently which can, indeed will, amplify inherent existing weaknesses:
A broken authorization check that might have resulted in limited data exposure when exploited manually can now be abused repeatedly and systematically by an AI-driven process.
The implication for enterprises is critical: APIs are no longer just integration points—they are control surfaces for autonomous systems. AI adoption without mature API security multiplies risk faster than most organizations realize.
For large enterprises, the report’s findings point to several clear implications:
As if it needed to be said, but security and engineering teams need to work together more closely than ever—developers defining intent and functionality, security teams defining guardrails and enforcement.
The State of API Security Report 2026 doesn’t reveal a brand-new threat landscape—it confirms that the same fundamental API security issues continue to cause the most damage. What’s different now is the context: APIs sit at the center of digital transformation, cloud-native architectures, and AI-driven systems.
For large enterprises, the message is clear. Fixing API security basics is no longer an optional nice to have, doing so is a prerequisite for safely scaling AI. The organizations that succeed in 2026 will be those that treat APIs not just as interfaces, but as governed, enforceable security assets across the full lifecycle.
﹡State of API Security Report 2026
The State of API Security 2026 report delivers a data-driven analysis of real-world API vulnerabilities, showing how common mistakes in implementation translate into security risks in production. We draw on extensive vulnerability and exploit cases, as curated by our APIsecurity.io editorial team over two years, to highlight the most common API flaws, from broken input validation and missing authentication to operation-level authorization failures.
Point the 42Crunch MCP scan at any MCP server and receive a scored report against the OWASP MCP Top 10 and your regulatory frameworks in under 60 seconds. No agent, no deployment, no commitment required.